NIST IAL3 Identity Proofing for FedRAMP High (Class D): Controlled Kits and Kiosks
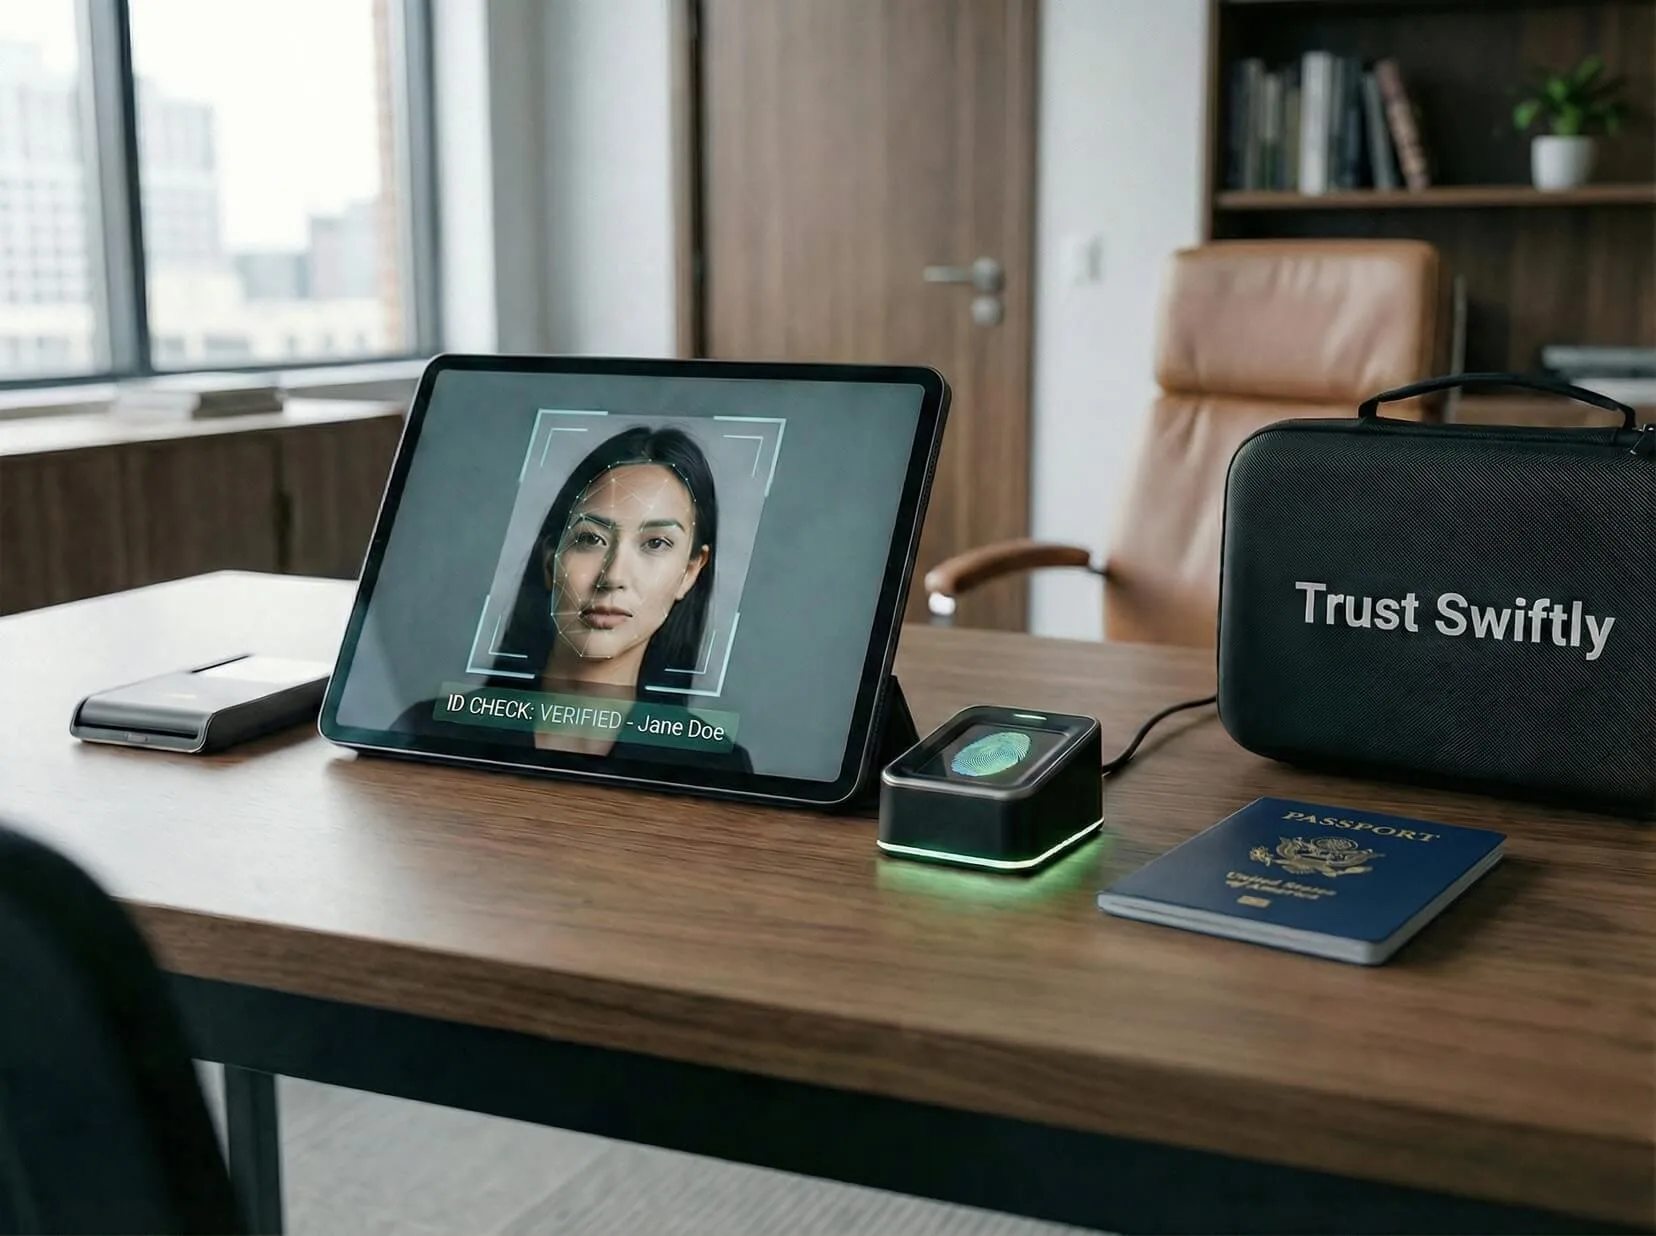
Attended NIST SP 800-63A-4 IAL3 proofing at your office or home, no travel, built for FedRAMP High (Class D) programs: high-risk users, remote hires, contractors, and privileged access. Ship IAL3 Kits from what we believe is the largest dedicated IAL3 fleet, or deploy office kiosks. A trained Trust Swiftly agent attends every session, and you receive a signed evidence package your independent assessor can review.
Need to validate the workflow? Request a pilot kit.
Federal agency or contractor buyer? See the federal identity proofing page.
- 200+
- IAL3 Kits in what we believe is the largest dedicated fleet
- 50 states, 32+ countries
- Kits ship to homes and offices, no fixed enrollment center
- Every session
- Attended live by a trained Trust Swiftly agent
- Zero
- Session data stored on the device; evidence is sealed server-side
IAL3 Requirements Under NIST SP 800-63A-4
NIST IAL3 is the highest identity assurance level in SP 800-63A-4: identity proofing performed on-site and attended by a proofing agent, with biometric collection and retention added to the IAL2 steps.
IAL3 identity proofing SHALL only be delivered as on-site attended. The proofing agent MAY be co-located with the applicant or attend the identity proofing session via a CSP-controlled kiosk or device.
SP 800-63A-4 §4.3.1For identity proofing at IAL3, the CSP SHALL collect:
One piece of FAIR evidence and one piece of STRONG evidence
,Two pieces of STRONG evidence
, orOne piece of SUPERIOR evidence.
§4.3.2The CSP SHALL collect and retain a biometric sample from the applicant during the identity proofing process
§4.3.3The CSP SHALL monitor the entire identity proofing session through a high-resolution video transmission with the applicant.
§4.3.8The CSP SHALL have a live proofing agent participate remotely with the applicant for the evidence collection, evidence validation, and verification steps of the identity proofing process.
§4.3.8Upon the successful completion of identity proofing at IAL3, the CSP SHALL send a notification of proofing to a validated address for the applicant
§4.3.9The CSP SHALL distribute or enroll the subscriber’s initial authenticator during an on-site attended interaction with a proofing agent.
§4.3.10
In these requirements, the CSP (credential service provider) is the proofing provider. Trust Swiftly runs IAL3 sessions to these requirements, on a controlled IAL3 Kit or kiosk at an approved office or home with a trained agent attending. Every requirement, explained: What Is NIST IAL3?
Start today with IAL2, finish with IAL3 when the kit arrives. Run the IAL2 pathway now, at its own lower assurance level, and complete IAL3 once the IAL3 Kit reaches the user.
Why enterprise teams choose Trust Swiftly for IAL3
Assessor-Ready Evidence Package
Built for assessor review. Capture chain-of-custody records, session metadata, document evidence, and operator actions in one package your security team can map to IAL3 controls.
Enterprise Security Posture
Support regulated deployment requirements with documented controls, external security attestations, and configurable evidence retention.
What a Customer Told Gartner
“They sent IAL 3 Identity packages to our homes. We didn’t have to drive 4 hours to stand in front of a kiosk for 10 minutes.”
CloudOps Engineering Manager, verified Gartner Peer Insights review (opens in a new tab) of an IAL3 rollout for a FedRAMP High authorization.
The Enterprise Deployment Path for High Assurance
Coordinate hardware, proofing sessions, evidence capture, and reviewer access from one platform.
Your team gains defensible identity assurance without building a bespoke proofing operation.
Managed Logistics
Coordinate shipping, tracking, return flows, and device readiness so distributed users can complete high-assurance proofing without travel-heavy scheduling.
Cryptographic Certainty
Go beyond visual inspection with hardware-assisted capture, liveness checks, face-to-document comparison, and NFC chip validation where supported.
Built for FedRAMP High (Class D)
Support FedRAMP High (Class D) and other regulated environments with evidence packages, retention controls, and deployment patterns that security reviewers can inspect.
Scale or Segment: Two Ways to Deploy IAL3 Proofing
Choose the proofing model that matches your population, risk tier, and security boundary.
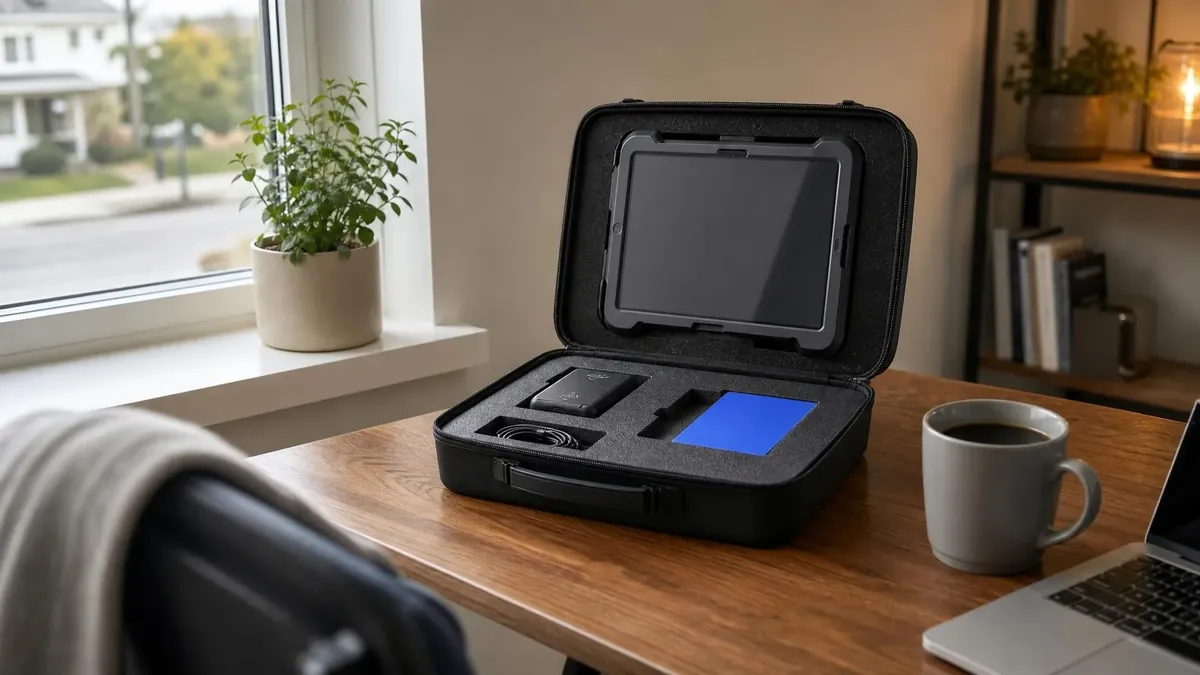
For Distributed Teams and Remote Hires
Use managed controlled hardware for attended proofing of rural, remote, or work-from-home users across the United States.
-
Step 1: Secure Chain of Custody. We track and mail the cryptographically secured kit directly to the verified individual.
-
Step 2: Verify. The user completes an attended IAL3 session on the kit at home or the office, typically in 3 to 10 minutes, with a trained agent attending over video.
-
Step 3: Return. User applies the prepaid label and drops it off.
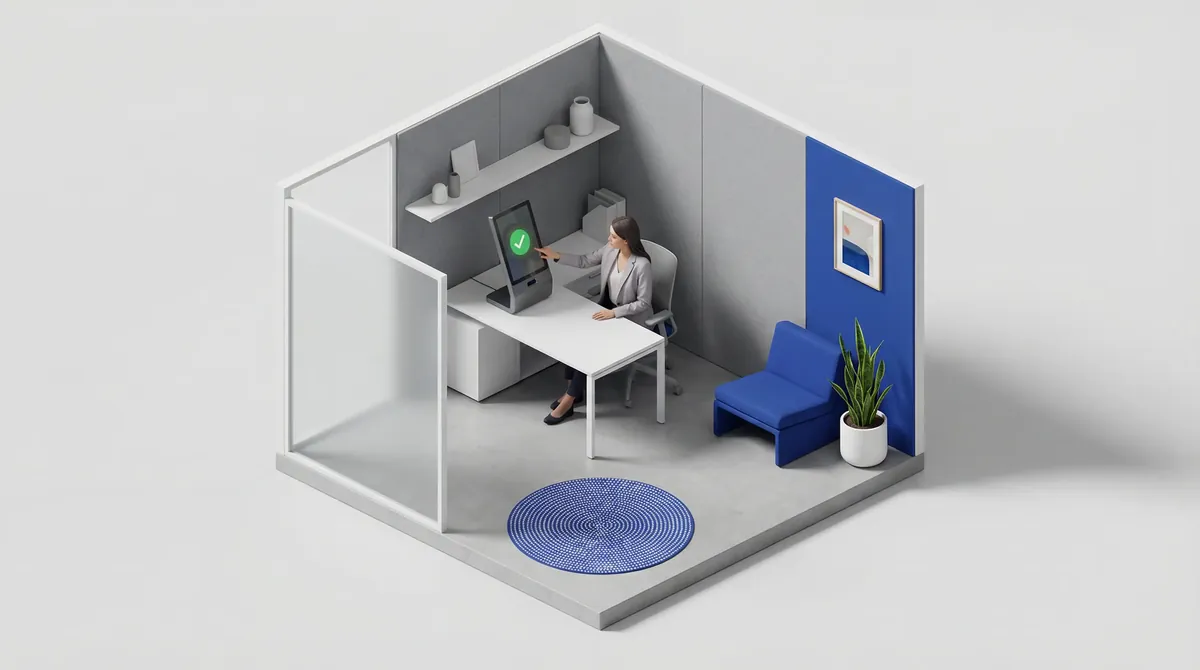
For HQ and High-Volume Sites
Turn your private rooms or a designated office into a verification center. Ideal for onboarding cohorts, SCIF access, and hybrid employees.
- Rapid Throughput: Verify large user groups each day with an on-site deployment.
- Flexible Hardware: Choose "Fixed" (bolt-down) or "Portable" (lock-away) units.
- Network Isolation: Operates on guest Wi-Fi or 5G, kept off your corporate network.
A More Defensible Model for IAL3 Identity Proofing
Compare travel-heavy enrollment with a controlled, hybrid proofing workflow built for distributed enterprises.
| Capability | Traditional Methods (Manual/Travel) | Trust Swiftly (Controlled Hybrid) |
|---|---|---|
| Deployment Speed | Weeks (Schedule travel/appointments) | Days (Overnight shipping / On-site) |
| Geographic Coverage | Limited to major cities | IAL3 Kit and kiosk coverage across the United States |
| Cost Structure | Unpredictable (Fee + Travel Stipends + Lost Hours) | Flat & All-Inclusive (Hardware + Logistics + Service) |
| Data Security | Public environments / Retail stores | Hardware-Anchored Trusted Path |
| Verification Tech | Manual Review / Basic Scanning | NFC Cryptography + Liveness Detection |
| Audit Trail | Paper-based / Disconnected | Centralized, tamper-evident evidence records |
| NIST SP 800-63A-4 Status | Difficult to Audit/Manual | Hardware-controlled evidence workflow |
Why NIST IAL3 Can't Run on an Applicant's Own Device
NIST SP 800-63A-4 sets the rule: IAL3 proofing is on-site attended only, on a location and devices the provider controls (Section 4.3.1). An applicant's own phone, webcam or laptop can't be used. See What Is NIST IAL3? for how it differs from IAL2.
When the user controls the phone, webcam, operating system, or camera feed, security teams have a harder time defending the chain of custody. Controlled hardware helps reduce injection, replay, and deepfake risk.
The Uncontrolled Device Gap
Software-only flows are harder to defend against virtual camera injection, replayed media, and device tampering when the applicant controls the endpoint.
The Controlled Capture Path
A controlled capture path gives reviewers stronger evidence of device custody, session integrity, operator supervision, and document authenticity.
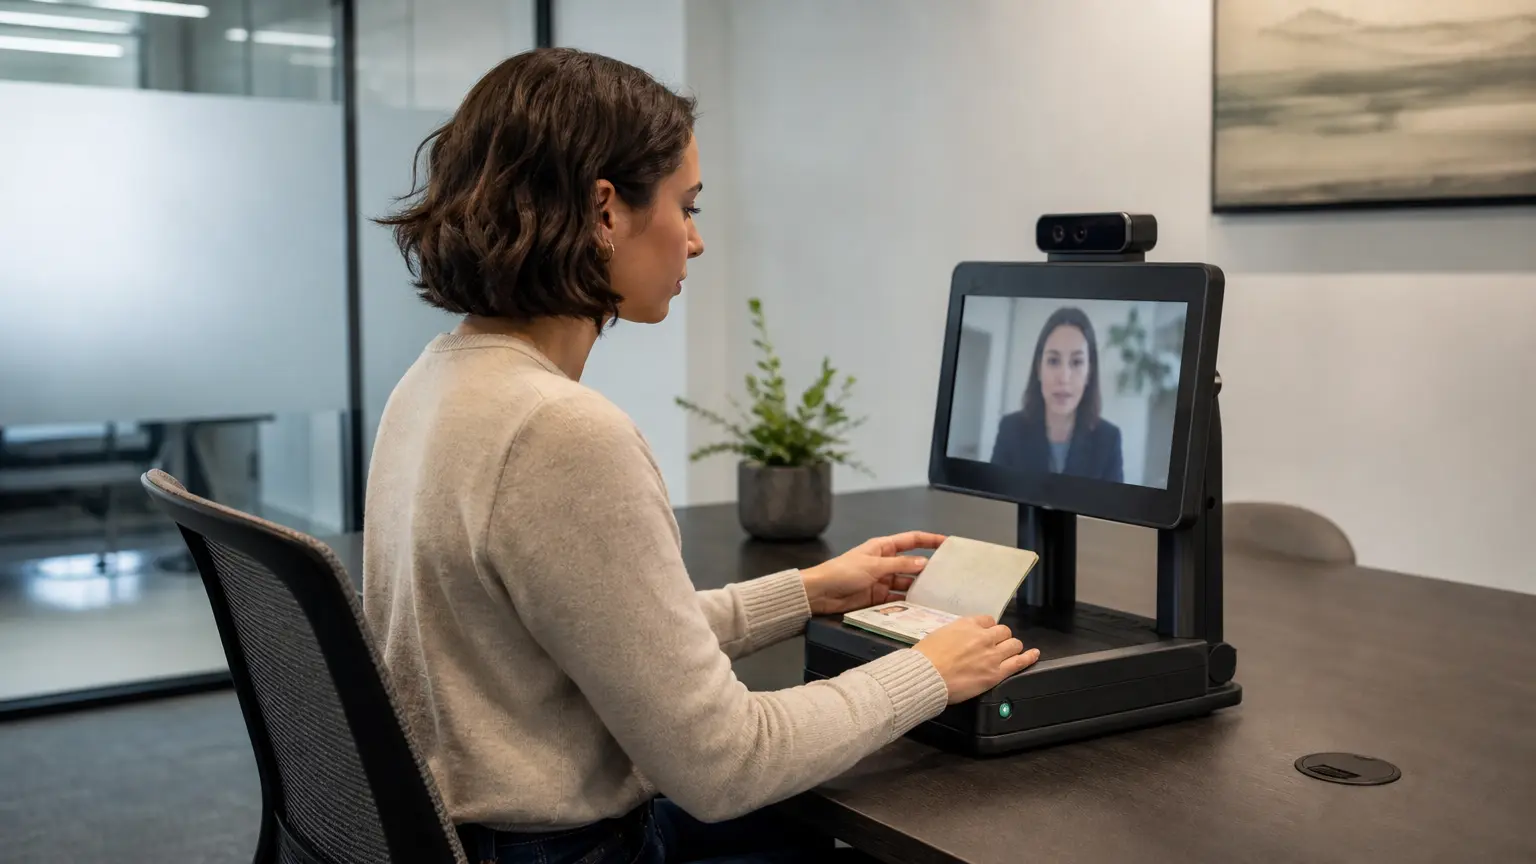
For Independent Assessors (Formerly 3PAOs)
Reviewing a FedRAMP High (Class D) package that relies on Trust Swiftly for IAL3? This is what each session gives you to test, and how to get the full mapping.
How a session meets SP 800-63A-4
Every IAL3 session runs on a Trust Swiftly kit or kiosk at an approved private location: a company office, a private office, or a private home workspace. A trained proofing agent attends every session over high-resolution video, which SP 800-63A-4 allows when the agent attends through a kiosk or device the proofing provider controls (Sections 4.3.1 and 4.3.8). The conformance criteria guide walks through all 24 IAL3 controls.
What each session's evidence package contains
- The proofing outcome
- Evidence validation and verification results
- Presentation attack detection results, conformant to ISO/IEC 30107-3:2023
- The proofing agent's record and the kit's chain-of-custody record
- The retained biometric
- The identifier of the authenticator bound during the session
A redacted sample package, built from a synthetic identity, is available on request.
IA-12 in the High baseline
The NIST SP 800-53B High baseline, which FedRAMP High builds on, includes IA-12 and enhancements (2) through (5). The control text, quoted from NIST SP 800-53 Rev. 5:
| Control | Control text |
|---|---|
| IA-12 Identity Proofing | “a. Identity proof users that require accounts for logical access to systems based on appropriate identity assurance level requirements as specified in applicable standards and guidelines; b. Resolve user identities to a unique individual; and c. Collect, validate, and verify identity evidence.” |
| IA-12(2) Identity Evidence | “Require evidence of individual identification be presented to the registration authority.” |
| IA-12(3) Identity Evidence Validation and Verification | “Require that the presented identity evidence be validated and verified through [Assignment: organization-defined methods of validation and verification].” |
| IA-12(4) In-person Validation and Verification | “Require that the validation and verification of identity evidence be conducted in person before a designated registration authority.” |
| IA-12(5) Address Confirmation | “Require that a [Selection: registration code; notice of proofing] be delivered through an out-of-band channel to verify the users address (physical or digital) of record.” |
FedRAMP's 2026 Rev5 control guidance adds, for Class D: authenticators “must be compliant with the most recent NIST Digital Identity Guidelines IAL, AAL, FAL level 3” (fedramp.gov). FedRAMP High Rev. 5 IAL3 Requirements maps each control to what a session record supplies.
Frequently Asked Questions
Does FedRAMP High require IAL3?
For Class D (High), FedRAMP's 2026 Rev5 control guidance says authenticators must comply with the most recent NIST Digital Identity Guidelines at IAL, AAL and FAL level 3, so the users in scope need IAL3 identity proofing. FedRAMP High Rev. 5 IAL3 Requirements gives the full answer, control by control.
Can NIST IAL3 be completed at our office or at home, without travel?
Yes. NIST SP 800-63A-4 delivers IAL3 as on-site attended proofing, and the proofing agent may attend through a kiosk or device controlled by the proofing provider (NIST calls it the credential service provider, or CSP). Sessions run at an approved private location, such as a company office or the user's home office, never a public place. Each session runs on a Trust Swiftly-controlled IAL3 Kit or kiosk with a trained agent attending, and kits ship to all 50 US states and 32+ countries.
How long does an IAL3 rollout take, from first call to evidence?
A specialist scopes your rollout within one business day. Each IAL3 Kit then ships to the user's approved office or home, the user picks a session time, and the attended session typically takes 3 to 10 minutes. Every completed session produces a signed evidence package, and the kit goes back on a prepaid label. Need someone started today? Run the IAL2 pathway now, at its own lower assurance level, and complete IAL3 when the kit arrives.
What do you keep after an IAL3 session, and for how long?
SP 800-63A-4 requires the provider to collect and retain a biometric sample at IAL3, so each session record keeps one alongside the evidence results. Each customer sets how long its IAL3 evidence is kept, to match its own policy and applicable law. Without customer instructions, the default in our Privacy Policy applies.
What happens if an IAL3 Kit is lost or damaged?
Every kit is tracked in transit both ways and inspected when it comes back, and the inspection is recorded. A damaged kit is removed from service. Kits hold no session data, so a lost kit exposes no proofing records.
Is there an IAL3 certification for providers?
No, as of October 2026. NIST publishes the IAL3 requirements in SP 800-63A-4 but states that it does not conduct certification or conformity assessment against them; agencies and assessors evaluate each provider directly. We give your assessor the IAL3 conformance mapping under NDA and a signed evidence package for every session.
What if a user misses their IAL3 session?
They pick a new time in the Trust Swiftly user portal and can reschedule without involving HR or security. A trained agent attends whichever session they choose.
Can we use both IAL3 Kits and office kiosks?
Absolutely. Most enterprise clients use kiosks for HQ staff and IAL3 Kits for distributed workers. All data flows into a single dashboard for unified auditing.
What happens if a user does not have a passport?
Two pieces of STRONG evidence, or one STRONG and one FAIR, also meet the IAL3 evidence requirement, so a REAL ID driver's license paired with a second strong document, such as a Permanent Resident Card, works. A trained agent attends the session either way.
Who manages the in-office kiosk?
We handle the software and security remotely via our management technology. You designate an on-site custodian, such as an office manager, to ensure physical safety and power. Temporary setups are also available to avoid management on-site.
How is NIST IAL3 priced?
As a platform license fee plus a fee for each completed IAL3 session, which covers the kit, two-way shipping, the attended session and the signed evidence package. The authenticator is priced separately. That lets you compare full program cost with travel-based proofing instead of per-check fees. See pricing.
What evidence does NIST SP 800-63A-4 require for IAL3?
Under NIST SP 800-63A-4, IAL3 carries the same evidence threshold as IAL2: one piece of SUPERIOR evidence, or two pieces of STRONG evidence, or one STRONG plus one FAIR. A SUPERIOR document such as an NFC ePassport satisfies the bar on its own, while a Real ID driver's license paired with a second strong document also qualifies. What elevates the process to IAL3 is the on-site attended session on controlled equipment and mandatory biometric retention. Knowledge-based verification is not accepted as proofing evidence.
How does AAL3 hardware-authenticator binding work after proofing?
Once the attended IAL3 proofing session confirms the person, we bind a phishing-resistant hardware authenticator to the verified identity. This anchors every future login to the same cryptographic key, so authentication reaches AAL3 and the verified identity cannot be reused or replayed by someone else. The binding happens inside the same trusted session, keeping the chain of custody intact from proofing through ongoing access.
Review the IAL3 Operating Model in Depth
See the best-practice case for zero-travel kits, global coverage, in-office deployment, approved-location proofing, and recurring re-verification for proxy-employee risk.
Related IAL3 Research
Go deeper on the standards, controls, and audit evidence behind NIST SP 800-63A-4 IAL3 verification.
Start Your FedRAMP High IAL3 Pilot
Not ready for a full rollout? We scope a pilot within one business day and ship IAL3 Kits to your first users, so your compliance and security stakeholders test the real workflow.